The Strategic Shift Toward Combined Risk Governance
Operating isolated applications for enterprise governance, risk registers, compliance reporting, and business continuity creates operational blind spots during critical disruptions. When regulatory documentation lives in static spreadsheets while operational continuity plans sit in disconnected IT management tools, emergency response teams lose critical hours reconciling contradictory data points.
Modern operational resilience requires unified telemetry where threat discoveries immediately update operational playbooks and regulatory posture metrics. Consolidating governance, risk management, and continuity into single automated workflows bridges the gap between executive compliance mandates and tactical floor recovery, ensuring uninterrupted service delivery across all dependencies.
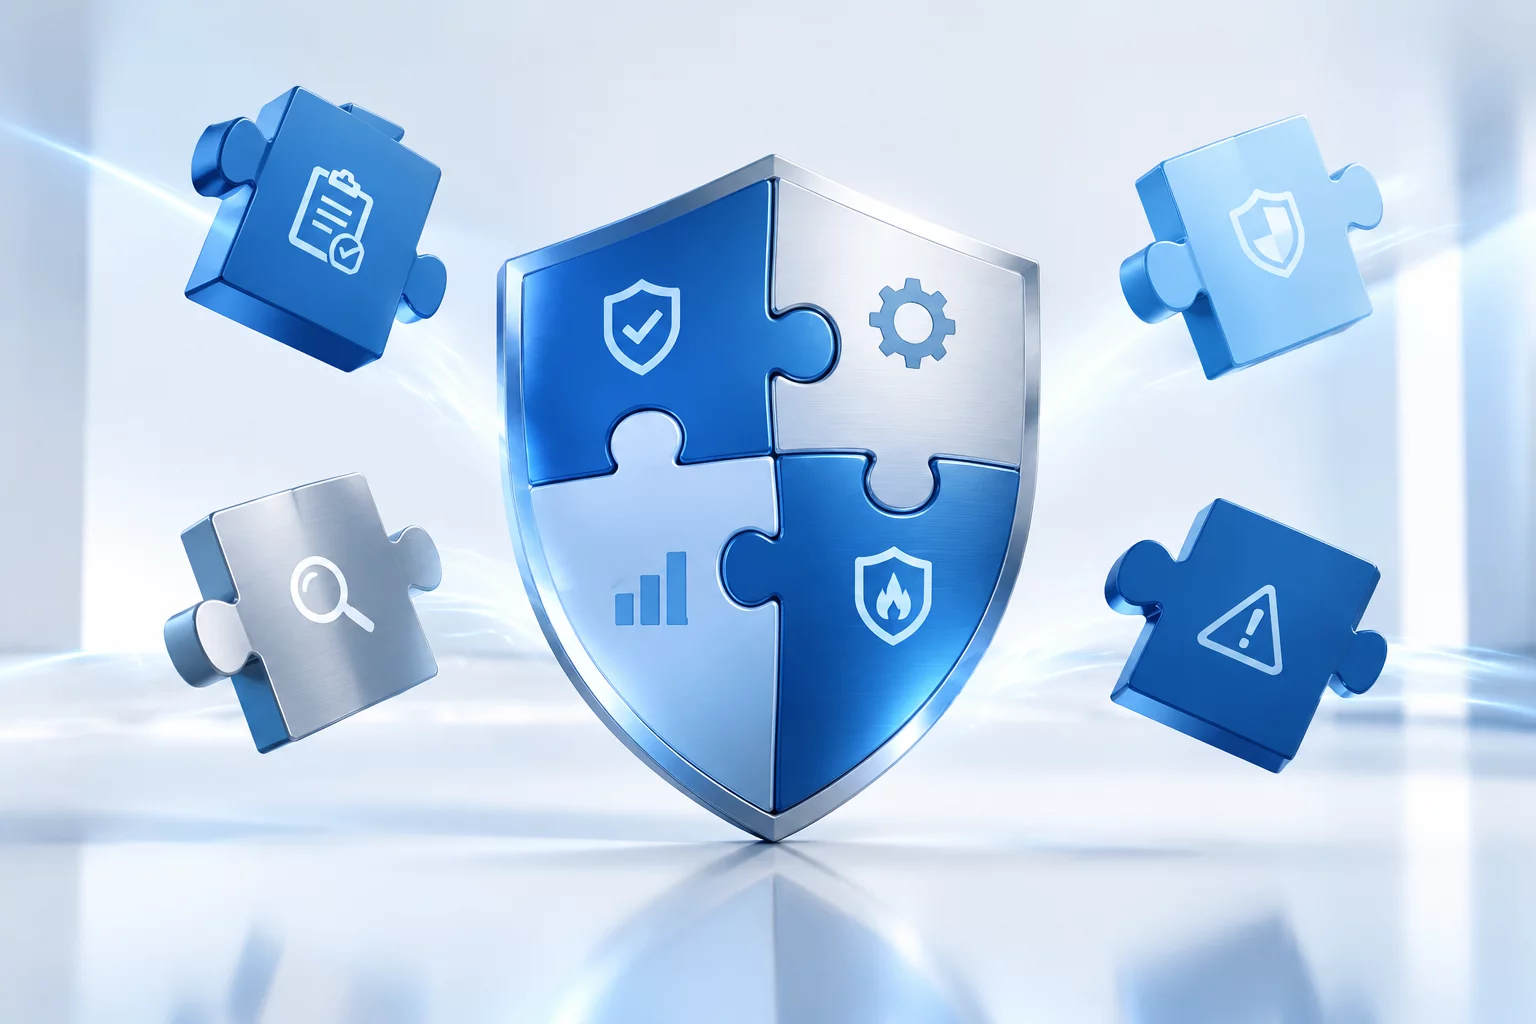
A consolidated GRC model transforms static compliance checklists into an active operational defense system, ensuring real-time business continuity when infrastructure shocks occur.
Pillars of an Integrated Continuity Architecture
Successfully unifying governance and continuity requires combining shared data schemas with automated operational triggers, built around two fundamental structural capabilities:
Unified Data Schemas
Centralize business impact assessments, asset registries, third-party vendor risks, and regulatory controls into one cohesive repository. This shared data foundation eliminates duplicate data entry and ensures that changing infrastructure dependencies automatically recalibrate organizational risk scores.
Dynamic Incident Triggers
Connect live monitoring metrics directly to continuity execution plans. When compliance thresholds drop or operational bottlenecks emerge, automated workflows immediately dispatch recovery tasks, notify accountable owners, and log immutable audit evidence.
Four-Step Implementation Roadmap
Transitioning fragmented risk protocols into a synchronized GRC environment follows a structured, phased implementation methodology:
Audit Inventory & Control Harmonization
Identify all active compliance obligations, operational recovery documents, and software tools. Map common controls across standards to eliminate redundant procedures and establish a common risk language across business units.
BIA and Workflow Integration
Combine Business Impact Analysis (BIA) questionnaires with daily operational metrics. Embed risk evaluation criteria into project planning tools so teams maintain continuous awareness of service criticality levels.
Telemetry Automation & Alert Synchronization
Deploy automated data connectors between core infrastructure monitors and the consolidated GRC dashboard. Automate notification pathways to ensure relevant team leads receive instant, actionable continuity instructions during disruptions.
Simulated Tabletop Drills & Verification
Run joint tabletop testing sessions involving compliance, IT operations, and executive leadership. Validate that automated plan activations function seamlessly under simulated blackout scenarios and refine documentation based on test findings.
Validation Benchmarks & Resilience Criteria
To verify that consolidated GRC risk management systems deliver measurable reliability, organizations should measure operations against these core technical benchmarks:
| Parameter | Operational Standard | Validation Criteria |
|---|---|---|
| BIA Refresh Cycle | Automated Continuous Sync | Real-time questionnaire scoring triggered by structural or technical modifications |
| Incident Escalation Latency | Under 120 Seconds | Simultaneous multi-channel notification dispatch across responsible role holders |
| Audit Trail Generation | Instant Automated Ledger | Full cryptographic logging of changes, drill exercises, and incident remediation steps |
Ready to Unify Your Risk Architecture?
Connect with our continuity advisory team to streamline your risk management framework and build verified operational resilience.